Resolving SSL Configuration Error in Elasticsearch
By Abhishek, . 2 min read
In shortThis issue arises from conflicting entries in the SSL configuration section of the elasticsearch.yml file.
Introduction
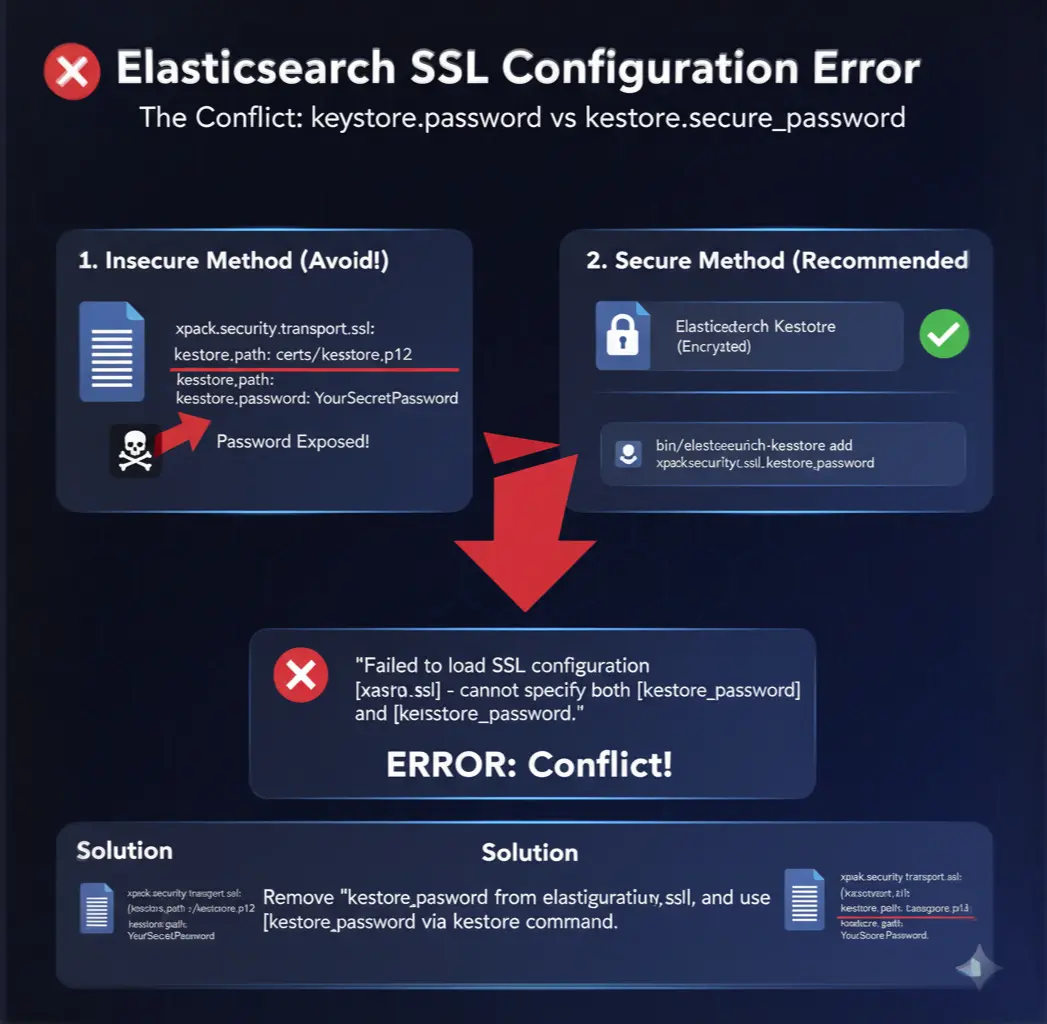
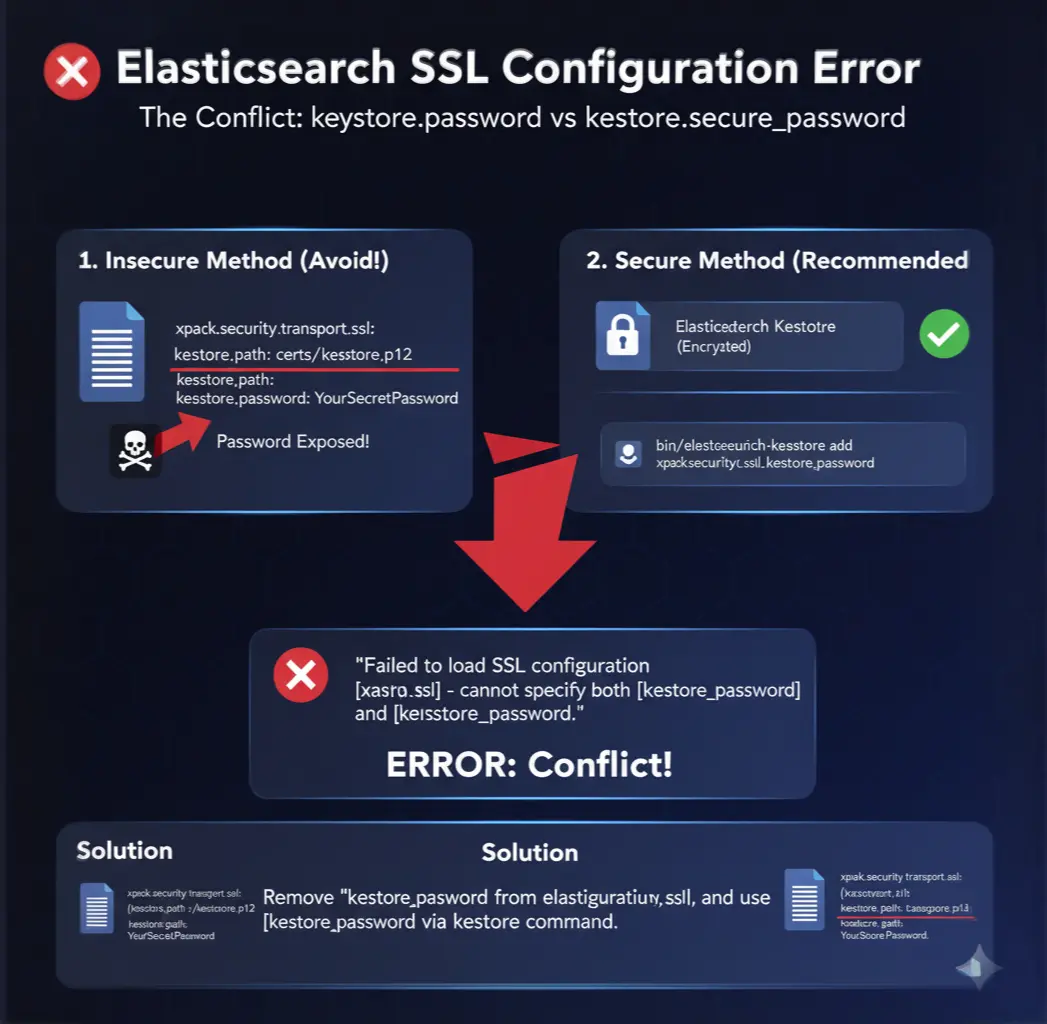
Elasticsearch requires a properly configured SSL setup to enable secure communication. A common configuration error is specifying both `keystore.password` and `keystore.secure_password` in the `elasticsearch.yml` file, leading to a conflict and preventing Elasticsearch from starting.
Problem Statement
You’re encountering the following SSL configuration error in Elasticsearch:
css
"Failed to load SSL configuration [xpack.security.transport.ssl] - cannot specify both [keystore.secure_password] and [keystore.password]."
This issue arises from conflicting entries in the SSL configuration section of the elasticsearch.yml file.
Proposed Solution
Fix the Configuration Conflict by removing the redundant parameter in the elasticsearch.yml file.
Steps to Implement
Locate the Configuration File
Open the elasticsearch.yml file using a text editor:
sudo nano /etc/elasticsearch/elasticsearch.yml
Edit the SSL Configuration Section:
Remove either keystore.secure_password or keystore.password.
Example of the corrected configuration:
xpack.security.transport.ssl: enabled: true keystore: path: certs/your_keystore.p12 password: your_keystore_password # OR # secure_password: your_secure_password
Save the File and Restart Elasticsearch:
Save the changes and restart the Elasticsearch service:
sudo systemctl restart elasticsearch
Verify the Fix:
Check Elasticsearch logs to confirm successful startup:
sudo journalctl -u elasticsearch | grep "started"
Why This Solution is Best
Quick and Direct Fix: Resolves the conflict without extensive reconfiguration.
Minimal Downtime: Only involves editing the configuration file and restarting Elasticsearch, ensuring services are back online promptly.
Preserves Existing Data: No need for creating a new cluster or other disruptive actions.
Alternate Solutions
1. Create a New Cluster
Steps:
Set up a new Elasticsearch cluster with correct SSL settings from the start.
Migrate data from the old cluster to the new one.
Pros:
- Provides a clean and error-free environment.
Cons:
- Time-consuming and may require additional resources.
2. Use Serial Console for Manual Fixes
Steps:
If the node is inaccessible via SSH, use a serial console to access the configuration files and fix the issue.
Remove conflicting entries and restart the service.
Pros:
- Useful when the node is in a non-responsive state.
Cons:
- Requires familiarity with serial console operations.
Conclusion
The SSL configuration conflict in Elasticsearch can be effectively resolved by removing redundant entries in the elasticsearch.yml file. This solution minimizes downtime and ensures secure communication without disrupting existing configurations. Alternate methods, such as creating a new cluster or using a serial console, can be used for more complex scenarios.
Proper SSL setup ensures the security and stability of your Elasticsearch environment, supporting seamless operations.
- elasticsearch
- devops
- cloud